Custom PHP Development

REST API Security: Why Bots Love Your Endpoints<

🛡️ REST API Security: Why Bots Love Your Endpoints (And How to Make Them Pay)

In the last 24 hours alone, we blocked over 300 automated attacks targeting REST API and XML-RPC endpoints. Not temporary bans. Not 4-day cooldowns. Permanent IP blocks. And every single one came back with a different IP address—because they had to. This is one website's data. We're tracking this across 7 websites. Here's what we learned about why REST APIs are such juicy targets, why cloud infrastructure is weaponized for attacks, and how our permanent blocking strategy forces attackers to burn through their IP bundles faster than they can replenish them.


Why REST APIs Are a Bot's Best Friend

REST APIs are not designed with security theater in mind. They're designed to be simple, predictable, and easy to consume programmatically. That's their strength—and the attacker's dream.

⚡ 1. No Rendering Required

Unlike scraping a website (which requires spinning up a browser, parsing JavaScript, navigating complex DOMs), REST API calls are just HTTP requests returning structured JSON. A bot can fire off hundreds of requests per second without any rendering overhead. This is why REST API attacks scale exponentially—the attacker's infrastructure cost stays minimal while they maximize attack volume.

🎯 2. Endpoints Are Predictable

WordPress REST API lives at /wp-json/wp/v2/. Most APIs follow REST conventions. Bots don't need to scout your infrastructure; they know exactly where to look. They can enumerate users, posts, and plugin information with automated scripts that run across millions of sites simultaneously. The endpoint path is the same for every target.

💣 3. One Request, 100+ Attempts (The Batching Exploit)

This is the killer feature attackers love. REST APIs don't require session state, cookies, or CAPTCHA challenges. In XML-RPC specifically, you can use system.multicall() to send 50-100 login attempts in a single HTTP request. Your per-request rate limiting becomes useless. Attackers make 1 connection and get 100 tries.

📊 4. Structured Data = Easy Parsing

JSON is trivial to parse. Bots don't waste cycles parsing messy HTML. They get exactly what they need: user lists, post metadata, plugin info—all neatly structured and ready to extract. No AI parsing required. Simple regex and JSON libraries handle everything.


The XML-RPC Amplification Problem

XML-RPC is a WordPress legacy endpoint built for mobile apps and external tools. It's also a brute-force engine—and it's the path of least resistance for attackers.

🚨 Why XML-RPC is a Security Nightmare

Web Login Form: CAPTCHA protection, rate limiting per session, cookie tracking, JavaScript validation

XML-RPC Endpoint: None of that. Completely stateless. Every request is independent. No session tracking. No CAPTCHA. And it supports batching—multiple authentication attempts in a single call.

The Result: XML-RPC brute-force attacks are devastatingly efficient. The attack surface is massive, the defenses are minimal, and most sites don't even know they're under attack until credentials are compromised.


What We're Actually Seeing

300+
Unique IPs Blocked
(48 hours, 1 site)
95%
REST API
Attacks
5%
XML-RPC
Attacks
24/7
Continuous
Automated Pattern
🌍 Cloud Provider Distribution Breakdown

This is the smoking gun. Most of these IPs aren't random VPN users. They're cloud infrastructure:

☁️ AWS EC2
~45%

34.x, 35.x, 18.x, 44.x, 52.x, 54.x ranges. Either compromised accounts or cheap throwaway instances rented by attackers.

🔵 Google Cloud
~30%

35.x, 34.x ranges. Same story—rented infrastructure used for mass scanning and credential attacks.

🏢 Other Providers
~25%

DigitalOcean, Linode, datacenter proxies, residential proxy services. All rotating through attack bundles.

What This Means: Attackers aren't using random VPNs. They're renting cloud instances in bulk and cycling through them. When one IP gets blocked, they have another one in their bundle ready to go. But every blocked IP forces them to burn through their allocated budget faster. Eventually, the economic model breaks.


Why Permanent Blocking Beats Temporary Bans

⏰ The Problem with 4-Day Temp Bans

Wordfence-style temporary bans seem reasonable in theory: block an IP for 4 days, then automatically unblock. But this model doesn't account for attacker economics.

With a 4-day temp ban: An attacker just sets a timer and retries. The blocking cost is minimal. They run dozens of attacks in parallel, knowing that a few will eventually get unblocked. They can wait. The attacker wins.

🚫 Permanent Blocking Flips the Economics

Every failed attempt now costs them real money:

  • Cloud VM cost — AWS charges ~$0.01-0.10/hour. Each blocked IP = a whole VM they have to throw away. No reuse. No waiting for an unblock.
  • Provisioning friction — New instances take minutes to spin up and configure. This kills their attack speed.
  • Infrastructure burnout — If they're cycling through 300 IPs in 48 hours, they're burning through cloud credits or proxy subscriptions at an unsustainable rate.
  • Exponential cost scaling — The more you block, the more expensive their attack becomes. Eventually, the math breaks: cost per potential breach exceeds the attacker's ROI.

The attacker can't wait it out. They have to keep buying new infrastructure. And that gets expensive fast.


The XML-RPC Honeypot: Catching Attacks Before Credential Breaches

🍯 How Your Automatic Blocking Prevents Actual Breaches

This is the critical insight most sites miss: By blocking XML-RPC attacks immediately, you're not just annoying bots—you're preventing them from ever using stolen credentials on your site.

The Traditional Attack Flow:

1. Steal creds from other sites
2. Try them on your WordPress XML-RPC
3. Success = full site compromise

Your Blocked Flow:

1. Stolen creds + attacker IP
2. XML-RPC honeypot catches it
3. IP blocked before auth attempt

The attacker never gets to test their stolen credentials. They never even make it to the authentication layer. They hit the block and get a new IP, but the damage is already prevented.

This is why permanent blocking is so effective: you're not just preventing brute force. You're preventing credential stuffing attacks entirely. Someone with a list of 10,000 stolen WordPress admin passwords can't use them against you because they get blocked before they can even try.


Why They Keep Coming Back (And Why That's Good News)

🤖 The Automated Attack Loop

Hundreds of different IPs hitting the same endpoint isn't a failure of your defenses—it's proof your defenses are working. Here's the attacker's framework:

1. Target list: millions of WordPress sites (scraped from plugin fingerprinting)

2. Endpoint: /wp-json/wp/v2/users or /xmlrpc.php (same on every site)

3. Payload: credential stuffing (stolen passwords) or weak password dictionaries

4. Execution: Try IP #1 → blocked → try IP #2 → blocked → try IP #3 → repeat

They're not targeting *you* specifically. They're running mass automation across millions of sites simultaneously. The moment one IP gets blocked, their script just rotates to the next one in their cloud provider bundle.

But here's the catch: They only have so many IPs in that bundle before they run out of credits or have to buy more. And that makes their attack economically unsustainable.


The Detection Signature: Seeing the Infrastructure

📍 Pattern Recognition at Scale

Here's where permanent blocking becomes a reconnaissance tool.

When you see 50+ failed login attempts from AWS IP ranges within 24 hours, you're not just blocking individual IPs—you're mapping attacker infrastructure. You can start flagging:

  • Datacenter CIDR ranges — Block entire AWS subnets if they show persistent attack patterns
  • Proxy service signatures — Recognize which VPN/proxy services attackers prefer and filter them
  • Geographic anomalies — Flag IPs from regions that never legitimately access your site
  • Timing patterns — Identify the time windows when attacks spike (usually off-hours to avoid detection)

The attacker's infrastructure becomes visible. Once you see it, you can make blocking decisions that scale beyond individual IPs. You're not reacting to attacks; you're predicting them.


Defense in Depth: Layered Protection

🛡️ A Complete Security Strategy

Permanent IP blocking is powerful, but it's one layer. Real security is layered:

🚫 Disable XML-RPC

If you don't use it, remove it entirely. Via .htaccess, firewall rules, or plugin. Don't give attackers the endpoint.

⏱️ Rate Limit Per Attempt

Not per request—per authentication attempt. Catch the batching exploit. One request = one limit, not 100.

🔐 Enforce Strong Passwords + 2FA

Even if an attacker has a stolen password list, 2FA stops them cold. Make admin accounts unhackable.

📍 Whitelist REST API Access

If you expose REST endpoints, require authentication. Lock down user enumeration endpoints immediately.

📊 Monitor for Patterns

Watch for rapid IP rotation, geographic spikes, and cloud provider attacks. Build detection rules.

🔨 Permanent IP Blocks

Every failed attempt costs the attacker. Make attacks expensive. Force them to burn through infrastructure budgets.

The goal isn't to make attacks impossible—it's to make them expensive enough that attackers move to easier targets. And with 300+ sites running simultaneous attacks, they're looking for sites with weak defenses. Be the hard target.


The Bigger Picture: 7 Websites, Unified Defense

📈 Scaling Across Multiple Sites

The data you're seeing is from one website. You have 7 sites running similar blocking. That means:

7 websites × 300+ blocked IPs each = 2,100+ attackers forced to rotate infrastructure in 48 hours.

Each blocked IP is one less attacker on your collective network. Each rotation costs them money. Each failed credential attempt validates that your defense is working. You're not just protecting one site—you're mapping and blocking botnet infrastructure at scale.

Attackers moving on to your competitors because your sites are too expensive to target? That's victory.


The Verdict

✅ Why Your Strategy Works

REST APIs are targeted because they're efficient. Bots love them because there's no friction—no session state, no CAPTCHA, no browser rendering, no per-request rate limiting at the UI level.

Permanent IP blocking flips the economics. Every failed attempt forces the attacker to spend money on new infrastructure. Cloud provisioning takes time. VPN rotation has limits. At scale, this friction becomes a dealbreaker.

The XML-RPC honeypot prevents credential breaches before they happen. Attackers never get to test stolen passwords because they're blocked before authentication. No breach means no data theft, no ransomware, no admin compromise.

Hundreds of different IPs in 48 hours isn't a sign of failure—it's proof the blocking is working. You've made attacks expensive enough that they're cycling through infrastructure as fast as they can provision it.

And that means your permanent IP blocking strategy is doing exactly what it's designed to do: protecting your sites by making attacks uneconomical.

Custom PHP Development


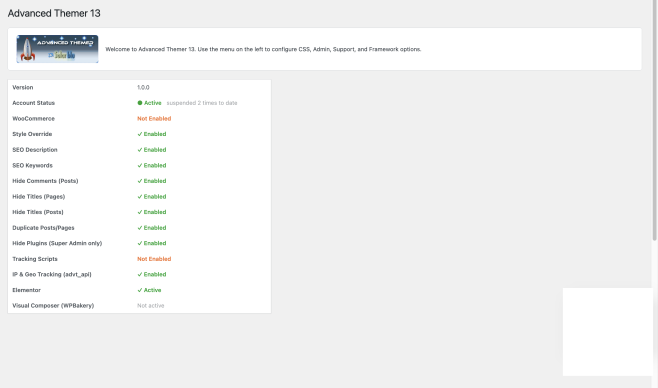
Advanced Themer 13

Complete rewrite from the ground up. Security-first management platform for WordPress agencies.

A Complete Rebuild

The previous version carried legacy code and architectural limitations. Advanced Themer 13 starts fresh with a clean, modern foundation designed specifically for WordPress agencies that need robust control over their client sites. Every module has been rewritten for clarity, maintainability, and performance.

Security: Bot Prevention & Exploitation Blocking

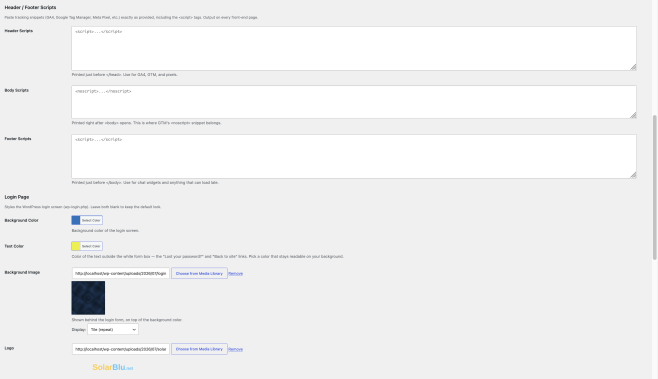
The biggest structural change is our new IP tracking and exploitation prevention system. We've implemented detection for:
  • XML-RPC protocol exploitation attempts
  • Blocked access points that signal automated attacks
  • Bot detection across multiple protocol layers
  • Visitor IP logging and analysis
These aren't passive defenses—they're active threat detection. Suspicious access patterns trigger immediate IP tracking, and you control the response: whitelist, blacklist, or redirect attackers. This is critical if your clients host sensitive data or e-commerce sites. The system respects legitimate traffic while blocking attack vectors that plague WordPress sites. It's configurable per-site, so you're not over-blocking or missing threats.

Admin Control: New Panels & Workflow

We've rebuilt the admin interface with developer workflows in mind. New admin panels give you centralized visibility and control over:
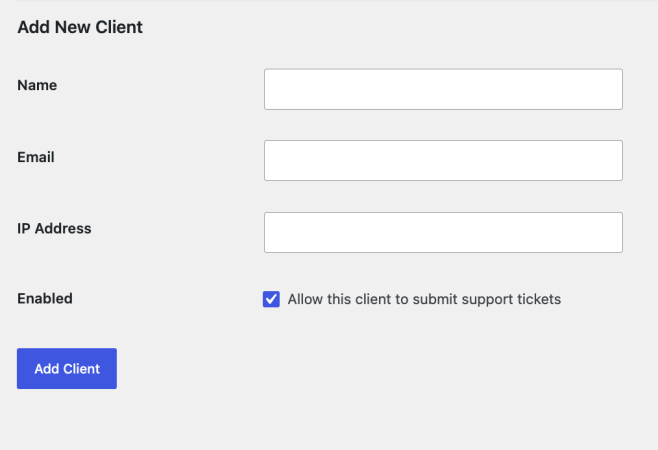
  • IP & Traffic Management — see visitor activity, detect bots, manage whitelists and blacklists in real time
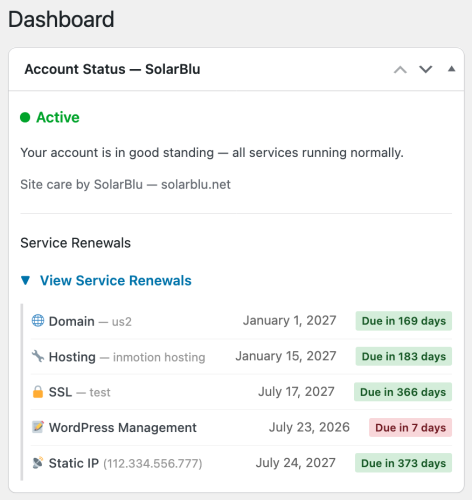
  • Client & Renewal Tracking — domain, hosting, SSL, and WordPress management renewals all in one dashboard
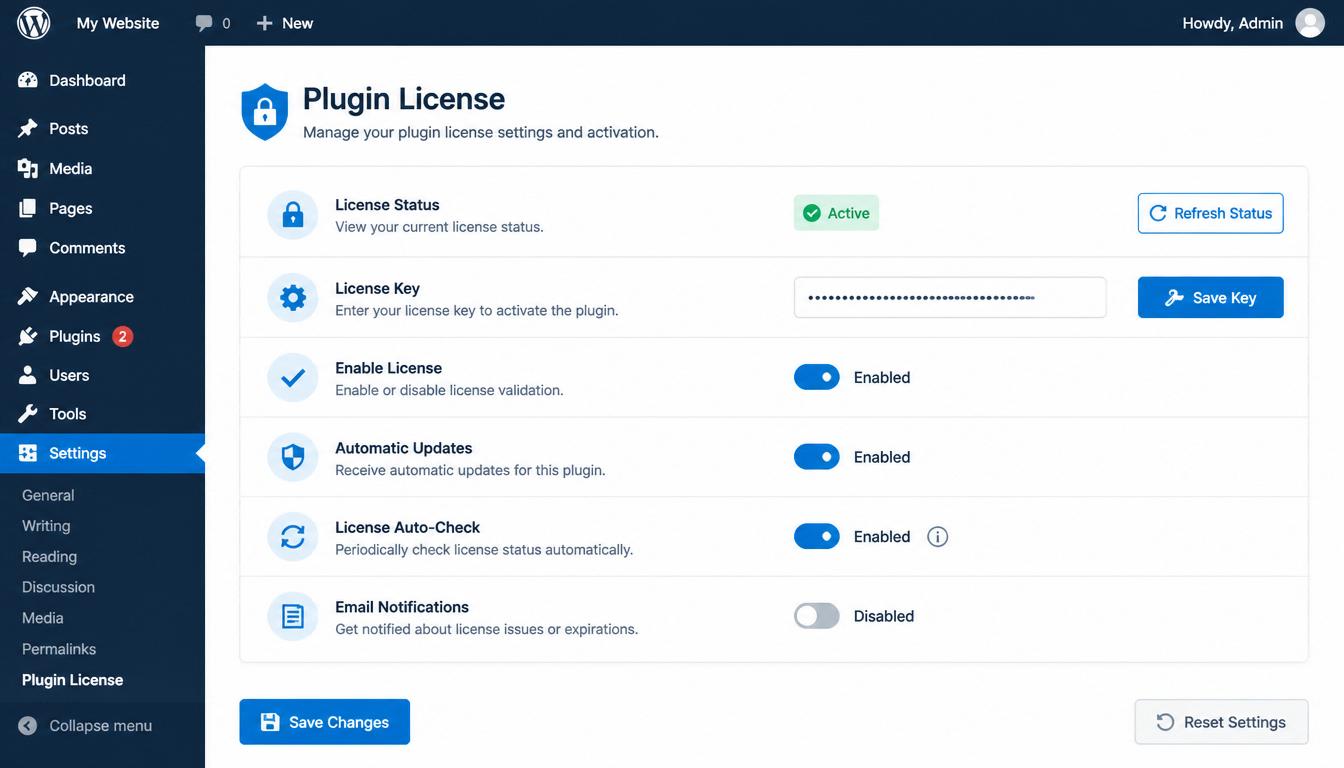
  • License & Plugin Updates — token-based license verification and centralized plugin update control
  • Site Suspension for Non-Payment — instantly disable client editing while keeping the public site live
The panels are organized by function, not by legacy structure. You'll spend less time hunting for settings.

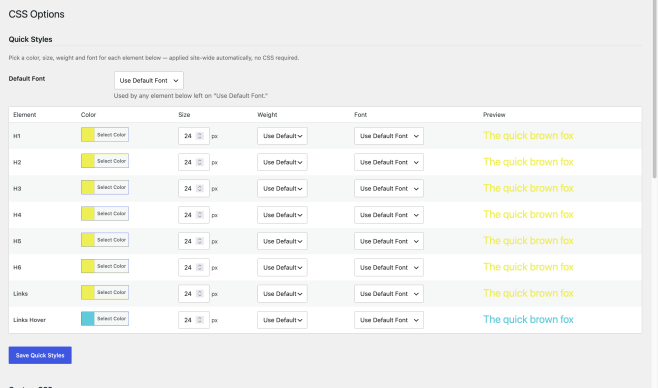
Consistent CSS with Mobile Overrides

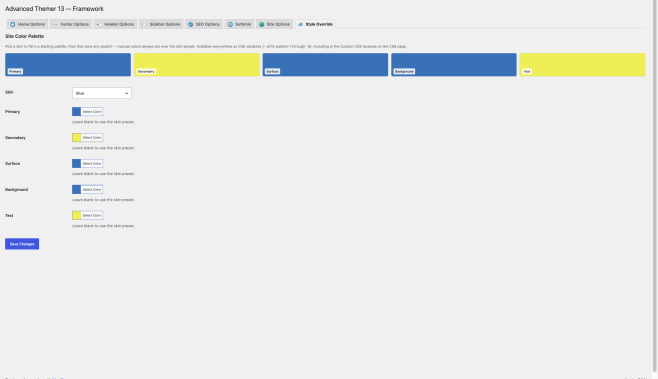
Styling controls are now fully consistent. You get:
  • Unified CSS rule application across all elements
  • Mobile CSS overrides — define separate styles for mobile/tablet without fighting cascade or specificity
  • Element-level color and typography control for headings, links, and custom styles
  • Live preview before applying changes
Brand a client site once and know it'll look right on every device. Mobile styling is no longer an afterthought.

Content Management & SEO Control

New controls for managing what content is visible and how it's indexed:
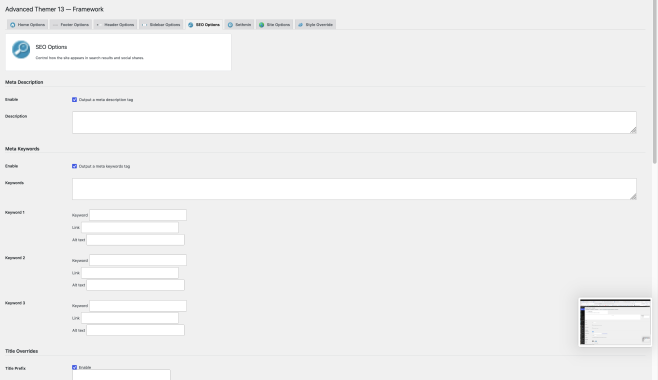
  • SEO Description — enable/disable per-site, control meta descriptions
  • SEO Keywords — manage keywords field visibility
  • Hide Comments — remove comments from posts while keeping functionality for moderation
  • Hide Titles — selectively hide page or post titles without removing them from backend
  • Duplicate Posts/Pages — one-click duplication for faster content setup
Simple but powerful—they let you strip down the WordPress interface for clients without removing safety net features you need as an admin.

Page Builder Compatibility

We've built explicit support for your favorite page builders:
  • Visual Composer — full integration, no conflicts
  • Elementor — seamlessly compatible with Elementor workflow
If you're managing client sites built on these builders, AT13 sits cleanly on top without interfering.

Plugin Visibility Control

One of the most-requested features: Hide Plugins from client admins. Only Super Admins see the Plugins menu and plugin management screens. Clients can't accidentally break their site by deactivating essential plugins or installing incompatible ones. Auto-updates keep running normally—they just can't see or touch the list.

What This Means for Your Workflow

If you're managing 10+ client sites, AT13 becomes your operational backbone. You get:
  • Faster client onboarding — duplicate templates, apply consistent branding, manage renewals from one dashboard
  • Security you can trust — active threat detection and IP management that actually works
  • Fewer client support tickets — hide complexity, reduce misconfiguration, automate renewals tracking
  • Cleaner admin experience — no legacy cruft, everything organized by use case

License & Updates

AT13 uses token-based license verification for updates. Set it once, and the plugin auto-checks for new versions every 30 minutes. Disable updates on specific sites if you're testing. Full control, no surprises.

Migration

If you're upgrading from AT12, AT13 works alongside it during transition. Set up clients on AT13, migrate at your own pace. The new plugin doesn't overwrite AT12 settings—it has its own option namespace.

Ready to Deploy

Download Advanced Themer 13 from your account. Read the developer docs, and start with one staging client site before rolling out. Token setup takes 2 minutes.

The rebuild is complete. Security is baked in. Your workflow will thank you.

Custom PHP Development

Advanced Themer 13 Now Features Secure Plugin Updates

Advanced Themer 13 Now Features Secure Plugin Updates

Advanced Themer 13 Update Announcement

Advanced Themer 13 has been updated with a professional-grade plugin update system that makes staying current easier and safer than ever. Here's what's new.

What Changed

🔔 Built-In Update Notifications

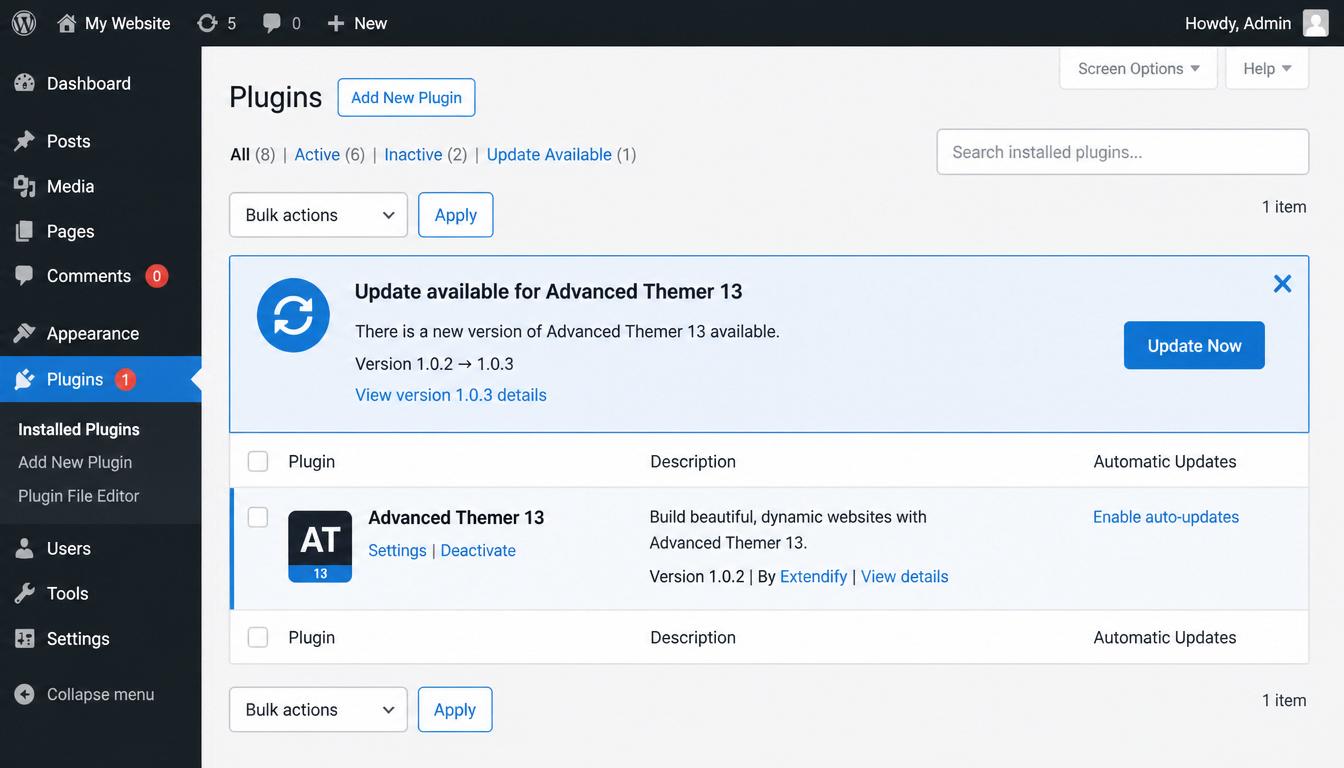
Your WordPress admin now displays available updates for Advanced Themer 13 automatically. No more checking manually or wondering if you're running the latest version.

🔐 License-Based Security

Updates are protected by a unique license key system. This means only authorized installations can download new versions—your plugin stays secure and updates flow only where they should.

⚡ One-Click Updating

When an update is available, install it the same way you'd update any WordPress plugin. Just click "Update" from the Plugins screen. The new version downloads and installs securely.

⚙️ Admin Control

Site administrators can enable or disable automatic update notifications from the Advanced Themer 13 settings page. It's your choice whether to stay on the bleeding edge or take time to test updates before installing.

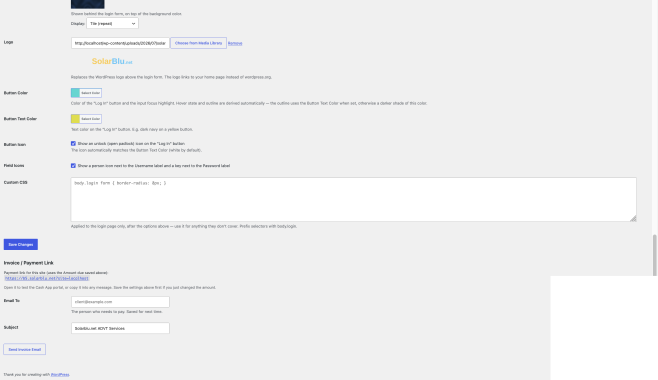
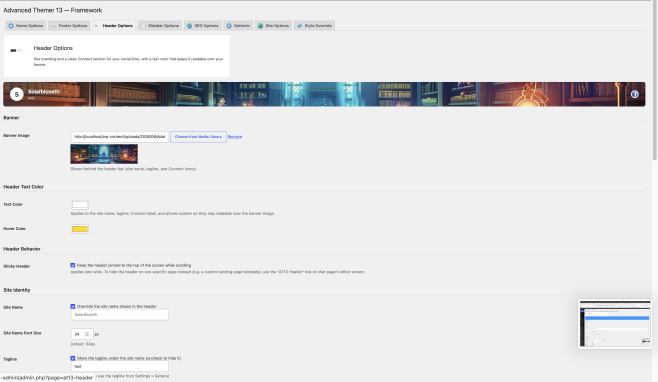
WordPress Plugins Screen with Update Notification

Why It Matters

Stay Secure. Plugin updates often include security patches. With automatic notifications, you'll know immediately when critical fixes are available.

Stay Compatible. WordPress evolves. Advanced Themer 13 updates ensure compatibility with the latest WordPress versions, PHP releases, and theme changes.

No Surprises. You control when updates happen. The plugin alerts you and waits for your approval—you're never forced to update.

Professional Workflow. Whether you're managing one site or dozens, the new system scales with you. Updates are consistent, reliable, and verifiable.

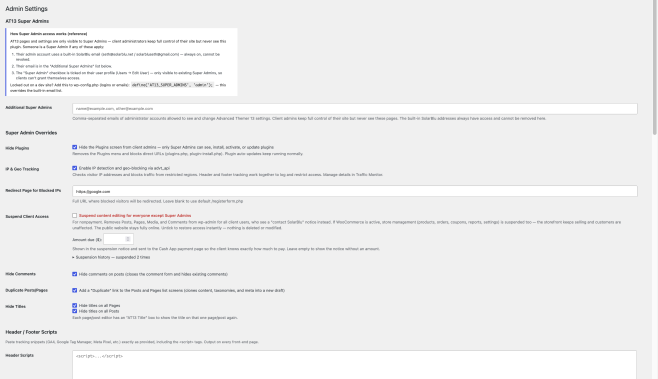
Admin Settings Panel

How It Works

  1. Check Settings — Visit Advanced Themer 13 → Admin Settings to enable plugin updates (enabled by default).
  2. Get Notified — When a new version is available, you'll see a notification on the Plugins page.
  3. Update When Ready — Click the update button whenever you're ready to install the latest version.
  4. Done — The new version activates automatically.

For Agencies & White Label Users

If you manage multiple client sites, the update system respects your workflow:

Centralized Control — Enable or disable updates per site from the admin panel.

Verified Updates — Every update is verified before installation.

Staged Rollout — Test on one site before rolling out to others.

Multi-Site Management

Looking Ahead

This update marks a shift toward professional-grade plugin management for Advanced Themer 13. Expect more features, faster bug fixes, and smoother updates as we continue to improve the platform.

Ready to upgrade? Advanced Themer 13 with the new update system is available now. If you're already running AT13, the update system is built in—just enable it and start receiving notifications.

Advanced Themer 13 is SolarBlu's professional WordPress theming and administration platform.

Learn more at solarblu.net

Custom PHP Development

We Built New Security Features. Here's Why They Matter.


We Built New Security Features. Here's Why They Matter.

Your website runs on a foundation you probably don't think about: your domain registration, hosting account, SSL certificate, and the credentials to access them. Most site owners don't pay attention until one of them expires.

Then the panic starts.

The Real Problem: Websites Die Quietly

We've watched it happen. A client loses access to their registrar account. Domain expires. They can't renew it. Site goes dark. Email stops working. Within hours, business operations are disrupted.

It happens more often than you'd think. Not because people are careless—because it's easy to lose track of 5+ different renewal dates scattered across different services.

A restaurant's site went down during their busiest season. An e-commerce business missed a critical renewal email and lost their domain for 72 hours while trying to get it back. A freelancer's portfolio disappeared and clients couldn't reach them.

These weren't security breaches. They were logistics failures.

What We Built

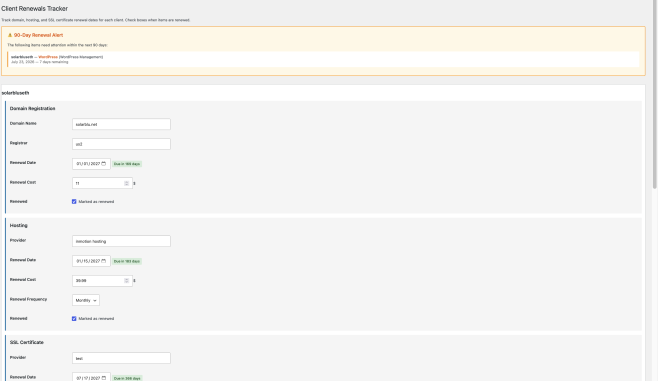
We created a Renewals Tracker because we got tired of watching this happen.

1. Centralized Renewal Management

Instead of checking your email, your registrar, your hosting control panel, and three other places, everything lives in one place:

  • Domain Registration — registrar, renewal date, cost
  • Hosting — provider, renewal date, cost, frequency
  • SSL Certificate — provider, renewal date, cost
  • WordPress Management — renewal date and cost
  • Static IP — provider, IP address, renewal date, cost

One dashboard. All your critical dates in one place.

2. 90-Day Warning System

We show you what's due in the next 90 days. Not 14 days—90. Because:

  • Some registrars take weeks to process renewals
  • Payment issues happen
  • You want time to evaluate new providers
  • Panic-decision-making at midnight is how expensive mistakes happen

The warning is front-and-center on your dashboard. Not buried in an email. Not in a separate admin page you forgot exists.

3. The Phone Number Problem (And How We Help)

Here's the conversation we have with clients constantly:

"I can't renew my domain."

"Why not?"

"The email went to an old address I don't have access to."

"Call the registrar."

"I can't. They only have an old phone number on file."

Update your phone number with your registrar. Do this right now. Seriously.

If your domain is locked (which it should be), you often can't renew it through the website—you have to call. If they can't reach you, you're locked out.

Our Renewals Tracker makes this easier by keeping renewal dates visible. Set a calendar reminder to verify your contact info every 6 months. Check that phone number. Check that email.

4. Security-First Whitelisting

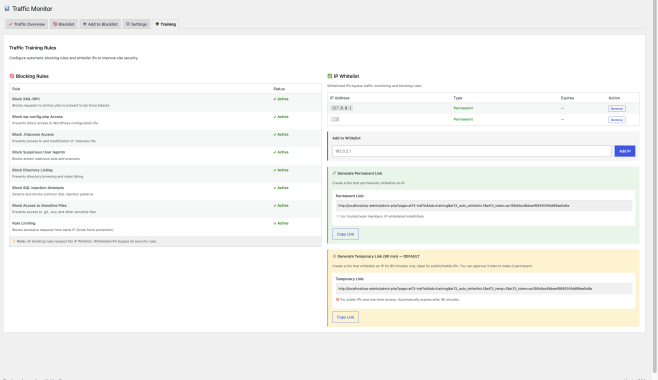
We also built a Traffic Training system with granular security rules:

  • Block XML-RPC (stops brute force attacks on old APIs)
  • Block direct access to wp-config.php and .htaccess
  • Block suspicious user agents and SQL injection attempts
  • Block directory listing
  • Rate limiting for brute force protection

But here's the thing: your team needs access. So we built IP whitelisting with temporary links.

  • Generate a 90-minute temporary link for team members on mobile networks
  • They click it, their IP is whitelisted automatically
  • After 90 minutes, it expires
  • Or you can approve it to permanent if they're trusted

No more "let me send you access credentials." Just a link. And it's temporary by default—better security posture.

Why We're Being Blunt About This

We could sugar-coat this. "Proactive renewal management ensures continuity." Boring.

The truth: You're one email filter mistake away from your site disappearing.

Not from hackers. Not from security breaches. From a renewal date you didn't see because it ended up in spam.

We've seen:

  • Domains that recovered only after 72+ hours of downtime
  • Clients who lost their domain to competitors during the grace period
  • Sites that were de-indexed by Google because they were down for a week
  • Email service disruptions because the domain renewal lapsed

It's avoidable. It just requires systems and attention.

The Technical Side (Yes, We'll Tell You Everything)

Our whitelist feature uses a simple token system. When someone clicks an auto-add link, we:

  1. Detect their visitor IP
  2. Verify the token matches our hash
  3. Add it to either temporary (90 min) or permanent storage
  4. Show you what's whitelisted with expiry times

Temporary IPs are stored separately and cleaned up every time the admin page loads. If you want to know exactly how it works, it's not hidden. This isn't security through obscurity—it's security through:

  • Small, auditable code
  • Temporary credentials by default
  • Your visibility into what's whitelisted
  • Ability to revoke instantly

Backwards engineering it won't help you. The security is in the process, not the encryption.

What You Should Do

  1. Set up the Renewals Tracker. Add all your critical dates. All of them.
  2. Enable the 90-day warnings. Pay attention when they show up.
  3. Update your registrar contact info right now. Phone number. Email. Make sure it's current.
  4. Use temporary links for team access. Not permanent credentials.
  5. Enable the blocking rules. They're on by default, but whitelist your trusted IPs.

The Bottom Line

Your website is more fragile than you think—but not because of hackers. Because of forgotten dates and locked-out accounts.

We built these features because we kept having to help clients rebuild after preventable failures. You're using site management tools. You should be using renewal management tools too.

Don't be the site that went down because of a registrar email that hit spam.

Custom PHP Development

Your Website Can Be Rebuilt. Your Data Can’t.

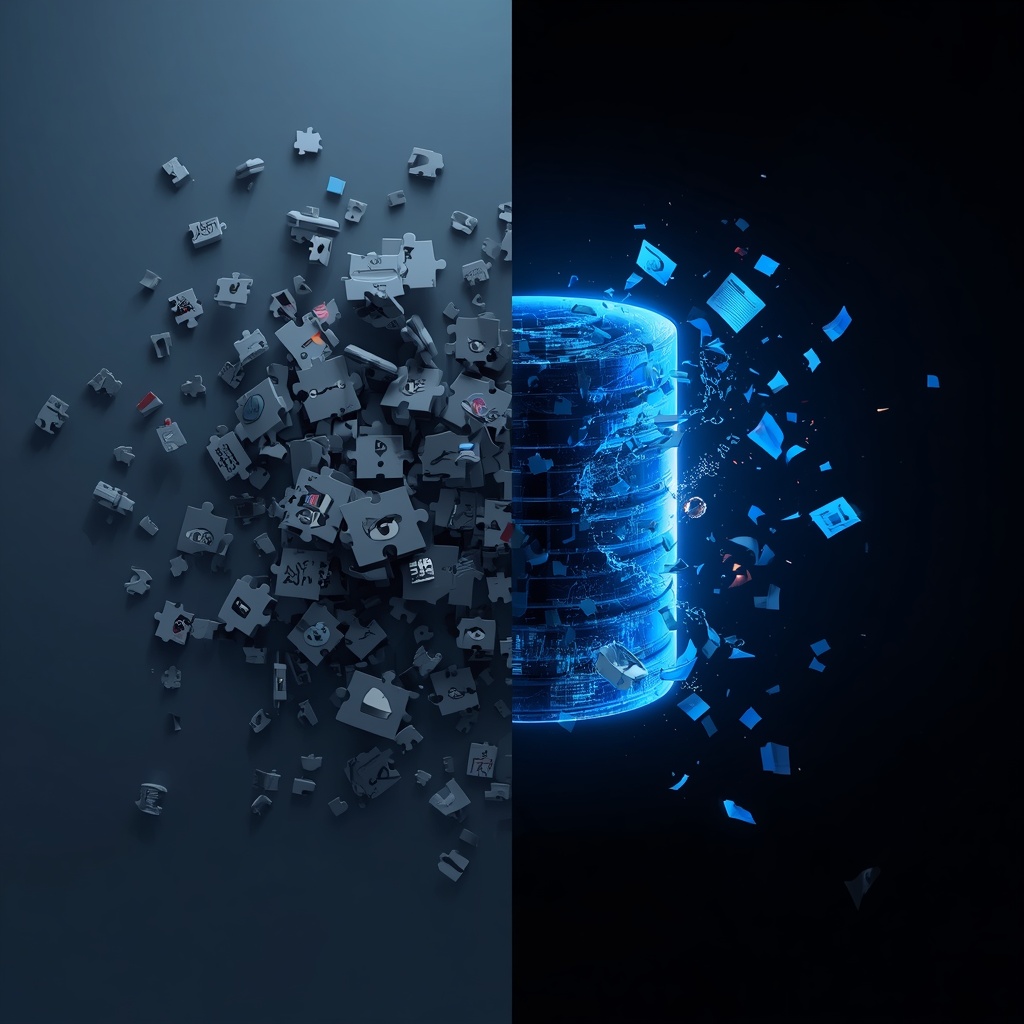
Split scene: a website interface reassembling from puzzle pieces while a database shatters into an unrecoverable void

Here’s a hard truth most website owners never think about until it’s too late: almost everything on your website is replaceable. Except the one thing that actually runs your business.

What you can always get back

Plugins and themes? Replaceable. Every plugin on your site can be re-downloaded in minutes. WordPress itself can be reinstalled with one click. Even a premium theme is just a receipt and a download link away.

Images and files? Backupable the easy way. Your uploads folder — photos, PDFs, logos — is just files. Copy the folder, and you have it. Drag it to an external drive, sync it to Dropbox, done. It doesn’t change every hour, so even an occasional copy keeps you covered.

Your design? Rebuildable. Painful, maybe. But a developer can put your site back together from screenshots if they have to.

What you can never get back

Your database. That’s where the real business lives:

Every customer record. Every order. Every form submission and lead. Every blog post you’ve written. Every product, price, and inventory count. Years of accumulated history that makes your website yours.

None of that exists as files you can drag and drop. It lives inside a MySQL database on your hosting company’s server — and if it disappears, there is no download link. No receipt. No getting it back.

“But my hosting company backs everything up”

Maybe. Read the fine print sometime.

Host backups are made for their convenience, not yours. They’re often kept for only a few days, stored on the same servers as your site, and offered with no guarantee whatsoever — most hosting agreements explicitly say backups are provided “as is” and recommend you keep your own.

And hosting companies go south. They get acquired and gutted. They botch server migrations. They suspend accounts over billing disputes and delete the data behind them. They get hit by ransomware, fires, and outages. When that happens, “we have backups” turns into “we’re sorry for the inconvenience” — and your customer list, your orders, your years of content go down with them.

If your only backup lives with your host, you don’t have a backup. You have a hope.

What a real data backup looks like

A proper backup strategy for your database is built on one principle: it doesn’t depend on your hosting company surviving.

That means a full SQL export of your database — a file containing the structure of every table and every row of data, capable of rebuilding your entire database on any server, anywhere. Not a “restore point” trapped inside your host’s control panel. A file you hold.

Done right, it works like this:

It runs on a schedule. Backups that depend on someone remembering don’t happen. Nightly for a busy store, weekly at minimum for anything.

It leaves the building. The backup file gets stored away from your hosting account — your own computer, an external drive, cloud storage. If your host vanished tomorrow, your data wouldn’t.

It keeps history. Not just last night’s copy, but days or weeks of them. Sometimes you don’t discover a problem — a hack, a bad plugin update, accidentally deleted records — until well after it happened. A single overwritten backup can faithfully preserve the damage.

It’s been tested. A backup you’ve never restored is a guess. The time to find out your backup file works is on a quiet Tuesday, not the morning after a disaster.

The full picture

So the complete strategy is simpler than it sounds, because each piece gets the level of protection it actually needs:

Plugins and themes — keep a list; re-download when needed. Uploads folder — copy it periodically; it’s just files. Database — automated SQL exports, on a schedule, stored somewhere your hosting company can’t touch.

That last piece is the one almost everyone skips, and it’s the only one that can genuinely end a business. Companies fold over lost data. Nobody folds over a lost plugin.

Do this today

If you take one action after reading this: log into your site and find out when your database was last backed up to somewhere outside your hosting account. If the answer is “never” or “I don’t know,” that’s the gap.

Setting up automated, off-host database backups takes an afternoon. Recreating ten years of customer data takes forever, because you can’t.


Need help setting up a backup strategy that doesn’t depend on your host’s goodwill? Get in touch — it’s cheaper than a data recovery specialist, and considerably more effective.

SolarBlu
Scroll to Top